Sanductor
Securely run Codex CLI and Claude Code without permission prompts under a sandboxed non-admin user with no access to your credentials, environment or home directory.
Free and open source
Apple silicon · macOS 26+
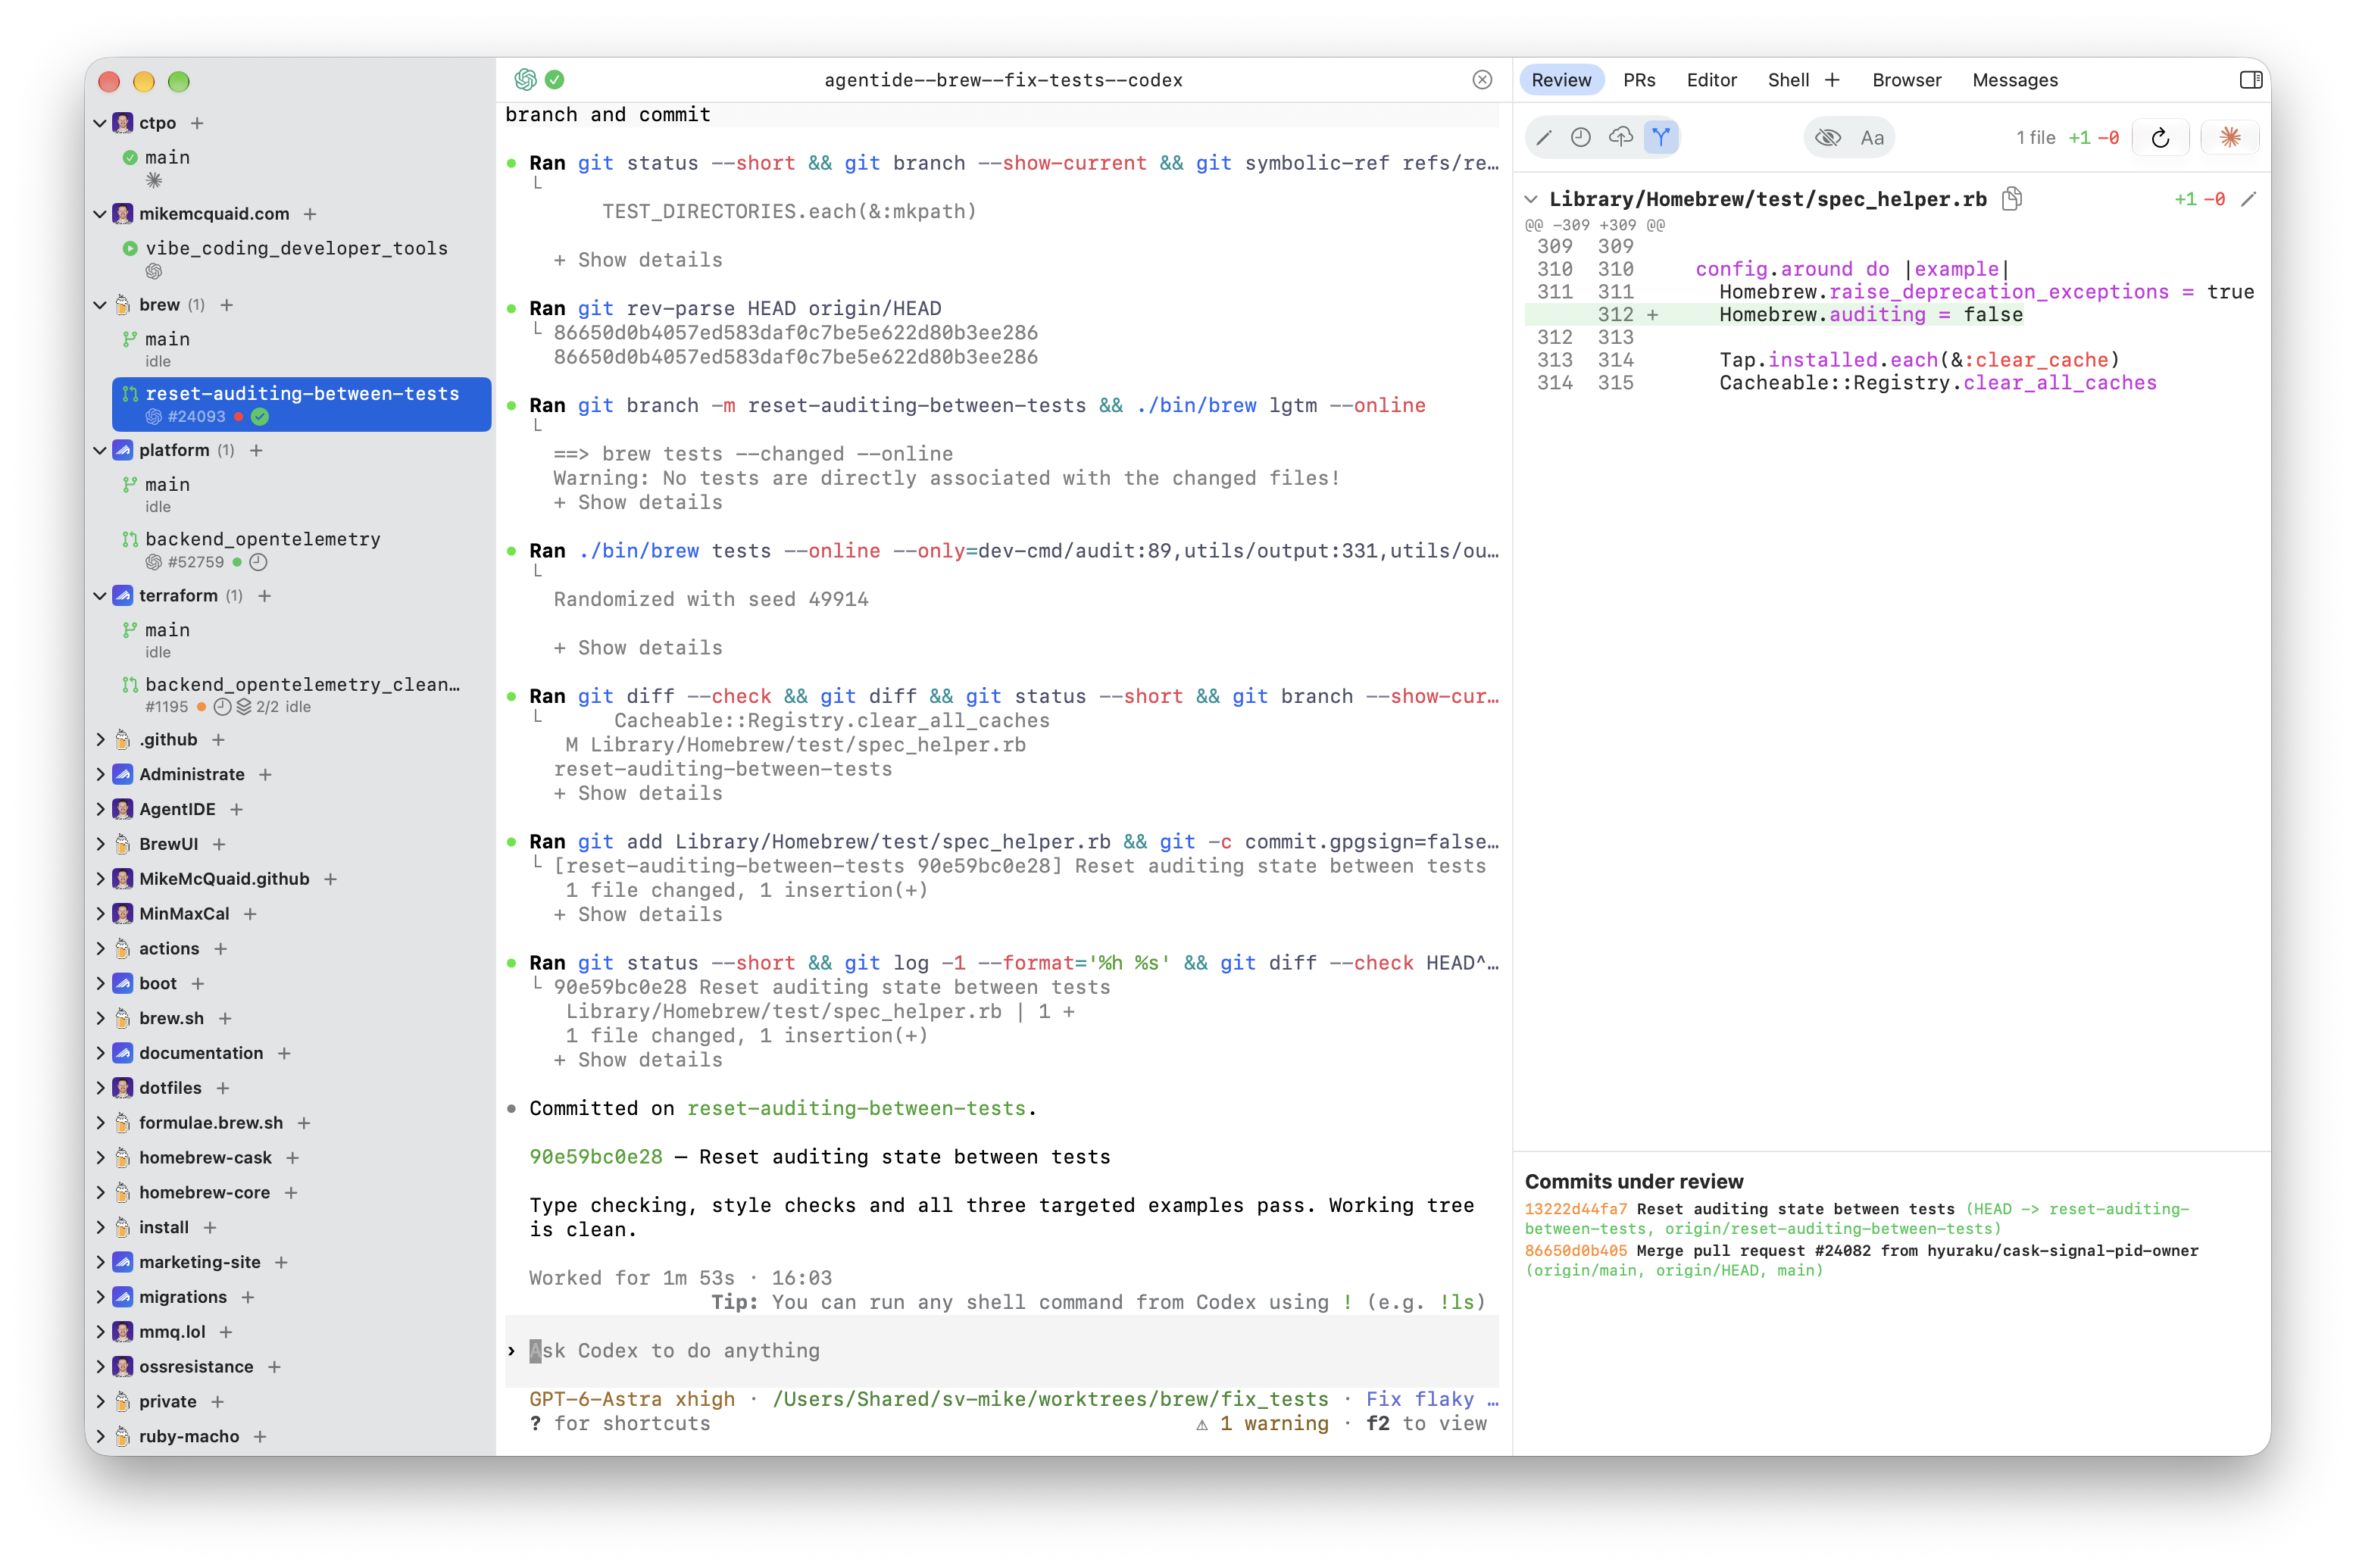
I wanted one native macOS app for the workflow I had spread across Superset, Fork and Zed. It has replaced Superset and almost all of what I used Fork and Zed for. I use it for almost all my work on Homebrew, beyond reviewing others’ PRs on GitHub itself.
No write access to my $HOME or GitHub
You know the “infinite monkeys with typewriters will eventually produce Shakespeare” idea?
Agents are the same.
Give an agent enough time and access and it will eventually sudo rm -rf / or, in my case, use a writable GitHub token to do bad things on Homebrew.
I don’t trust agents nearly enough to give them GitHub write access and neither should you.
My agents run in parallel Git worktrees as a sandboxed non-admin macOS user (sandvault-mike), separate from mine (mike).
They cannot access my home directory, GitHub credentials, signing keys or host environment variables through good old Unix permissions and user separation.
sandvault throws them in a sandbox too, for good measure.
That lets them work unattended without agent permission prompts.
My Sanductor workflow
I start from a prompt, GitHub issue, existing pull request or security advisory. When my agent is done, I usually review the code myself and reprompt as necessary. When I’m happy, I sign, rebase, push and open a pull request with one click. I then can wait for human or bot (e.g. CodeRabbit, Copilot) review or failing CI checks to pull these blockers into a prompt with one click. Alternatively, if I’m confident they will be good, I can enable “autofix” to apply them automatically.
Agents keep running and stay reachable over SSH (only as the non-admin user) when I quit the Mac app.
There is no Sanductor account, subscription or hosted relay, and I have no plans to add one.
You shouldn’t trust your agents and you shouldn’t trust a relay to be able to have this level of access.
Also, even if your SSH gets compromised somehow, remember that user has no GitHub write access anyway.
If interesting, I’ve written more about building Sanductor and my coding workflow.
Enjoy Sanductor!
Built on open source
Sanductor is free and open source under the AGPLv3 licence.
In the spirit of Unix philosophy, it combines small, effective standalone tools:
sandvault for user separation and macOS sandboxing,
herdr for persistent agent sessions,
gh for pull requests and
ripgrep for search.